-
Huijue switch port access VLAN
By default, an access port carries traffic for VLAN1; to set the access port to carry traffic for a different VLAN, use the switchport access vlan command. This chapter describes the configuration of access or trunk ports on Cisco Nexus 5000 Series switches. It includes the following sections: Ethernet interfaces can be configured either as access ports or a trunk ports, as follows: An access port can have only one VLAN configured on the interface; it. VLANs can be assigned based on interfaces, MAC addresses, IP subnets, protocols, and policies (MAC addresses, IP addresses, and interfaces). Table 3-69 compares different VLAN assignment modes. Use a console cable to connect to the switch or a network connection (like SSH) to connect remotely. Give the switch an IP address so that you can administer it. The switch's command-line. Configuring VLANs involves two main components: configuring the VLANs themselves, which refers to creating the VLANs on layer 2 (switches), and then configuring inter-VLAN routing, which is performed on layer 3 (routers).
[PDF Version]
-
Device Network Access Switch
An access switch is a network edge device that directly connects end-user hardware such as computers, IP phones, wireless access points, cameras, and IoT devices to the broader network. It typically sits at the access layer, provides high port density, often delivers PoE, and forwards traffic. The hierarchy Ethernet network is a three-layer integrated setup of networking devices. These networks are designed with three tiers that facilitate strategic installation, management, and maintenance, and so on.
-
Basic Security Configuration of H3C Access Switches
The Security Configuration Guide describes security fundamentals and configuration. It covers the authentication features (including AAA, 802. 1X, MAC authentication, portal authentication, and so on) and attack protection features (including IP source guard, ARP attack. To read the whole book, click the link below; to read the individual chapters, click the links on the left. Page 3 Preface The H3C S5120-HI documentation set includes 1 1 configuration guides, which describe the software. To create a user on an H3C switch, you can perform this operation through a web interface or SSH. Follow the commands below to create a user: Specify the user's access level. For instance, to grant the user full. In this video, we cover H3C switch configuration, including basic setup, VLAN configuration, IP address assignment, port settings, and switch management. These configuration guides also provide configuration examples to help you apply. Page 1 H3C S5830V2 & S5820V2 Switch Series Security Configuration Guide Hangzhou H3C Technologies Co. Page 2 SecPro, SecPoint, SecEngine, SecPath, Comware, Secware, Storware, NQA, VVG, V G, V G, PSPT, XGbus.
[PDF Version]
-
VLAN partitioning on access switches
A VLAN on Cisco switches segments a physical switch into multiple logical broadcast domains by assigning ports to VLANs. This isolates traffic within each VLAN, enhancing security and reducing broadcast traffic. VLANs improve network management and require routing for inter-VLAN. VLAN access control lists (ACLs) or VLAN maps access-control all packets (bridged and routed). VLAN maps are configured to provide access control based on Layer 3 addresses for IPv4. This lesson will focus on the first component, configuring the switches to. VLAN is a new data exchange technology that logically divides LAN devices (note, not physically) into network segments to realize virtual workgroups. This emerging technology is mainly used in switches and routers, but the mainstream application is still in switches. How do switches divide VLANs? If you don't know much about VLAN, this article can take you to learn more about VLAN, with detailed comments. Neithe ing is used to properly transmit multiple VLAN frames thro re a number of different ypes of VLAN attacks in modern switched networks.
[PDF Version]
-
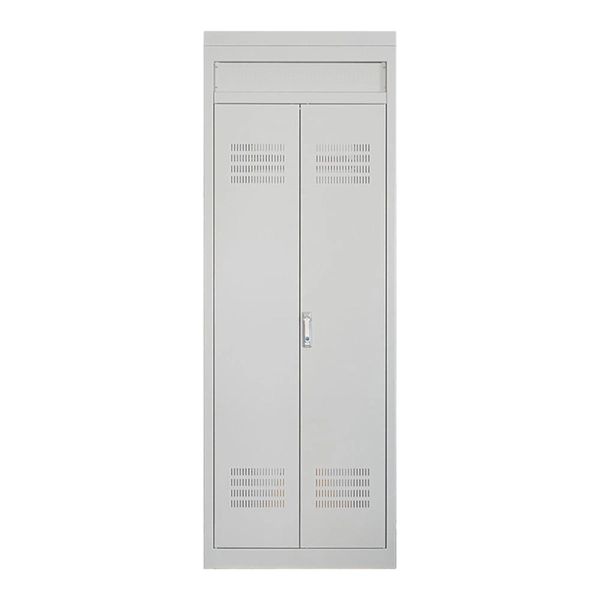
576 Fiber Optic Distribution Cabinet Three Networks
576 Port Fiber Distribution Hub (FDH) Cabinet Family | Weather-tight, secure outdoor FDH cabinet line featuring custom integration options. FDH cabinets offer fast deployment, easy installation, and flexible configurations without interrupting existing internet services. The 576 port FDH is ideal. The Cross Connection Cabinet (FDC) provides a secure transition point from the passive optical network (PON) to the subscriber drop for both pre-configured pigtail and/or patch and splice applications. Visit Insights Overview to get started. You are about to download a machine translated document. Description:Cross Connection Distribution Cabinet is designed for a cross connection between telecom feeder cable and custome Description: Cross Connection Distribution Cabinet is designed for a cross connection between telecom feeder cable and customer cable. China factory anti-theft 576F floor standing SMC 1450*755*543 double. 1. connecting distribution network and equipment cable.
[PDF Version]
-
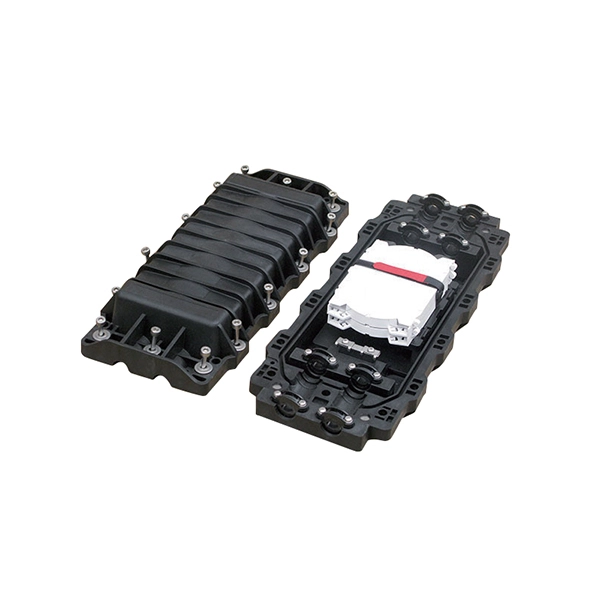
General Topology of Passive Optical Networks
PON primarily utilizes a point-to-multipoint topology and fiber optical splitters to transmit data from a single point of transmission to multiple user endpoints. The key advantages of PON lie in its ability to offer remote, high-bandwidth, and efficient network connections. A passive optical network (PON) is a fiber-optic telecommunications network that uses only unpowered devices to carry signals, as opposed to electronic equipment. In practice, PONs are typically used for the last mile between Internet service providers (ISP) and their customers. This network is suitable for building. on their deployment characteristics in developing access network architectures. Following dense wavelength division multiplexing (DWDM). simplicity of implementation and low OPEX [1, 2].